LLM security baselines
Hardened configuration standards for model access, context handling, logging and data retention.
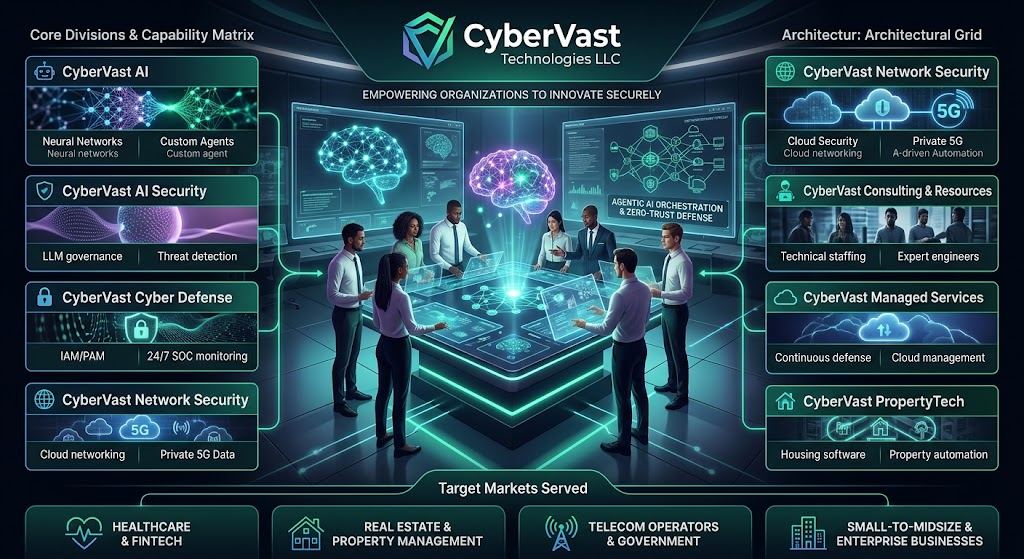
Large Language Model (LLM) security baselines, agent access guardrails, real-time AI threat detection, AI governance frameworks and secure AI system architecture.
Hardened configuration standards for model access, context handling, logging and data retention.
Least-privilege tool permissions, scoped credentials and approval gates on high-impact actions.
Monitoring for prompt injection, data exfiltration attempts, jailbreaks and anomalous agent behaviour.
Policy, model inventory, risk classification and review workflows your auditors can follow.
Reference designs with isolation boundaries between models, tools, data and untrusted input.
Adversarial testing of prompts, tools and agent chains before they reach production.
Every engagement is scoped against measurable outcomes agreed up front — not a fixed product list.
Discovery workshop and current-state review against your risk profile and objectives.
Target-state design and a phased roadmap sequenced by business impact.
Implementation by our engineers, or embedded alongside your team.
Ongoing monitoring, tuning and governance reporting as the estate evolves.
Agentic AI systems, custom AI agents, multi-agent orchestration, Agent-to-Agent (A2A) protocols, Model Context Protocol (MCP) integrations and enterprise AI process automation.
Explore division →Zero Trust architecture, Identity & Access Management (IAM/PAM), 24/7 SOC monitoring, SIEM/SOAR platform integration, cloud security and threat modeling.
Explore division →Tell us about your environment and objectives. We will come back with a practical, prioritised plan — no obligation.